Anyone who protects information and recognizes risks early can avoid typical attacks in the age of AI. You learn what matters when handling data, passwords, and access credentials securely.
30 min
Multimodal
Über 30 Sprachen
Teilnahmebescheinigung
Phishing, ransomware, and social engineering cause billions in damage to companies every year, and over 90% of all successful cyberattacks begin with human error. Employees must recognize threats, consistently apply protective measures such as 2FA and secure passwords, and respond correctly in the event of a suspected incident. Without this competence, every technical security measure becomes worthless.
00 Introduction and fundamentals of information security
01 Threats and attack vectors
02 Protective measures
03 Consequences of information security incidents
04 Information security in day-to-day work
05 Summary
06 Knowledge check incl. certificate of completion
The entire workforce that uses passwords and access credentials, modular and suitable as initial training for new employees and as an annual refresher.
Leading organizations trust Bridgly
.png)

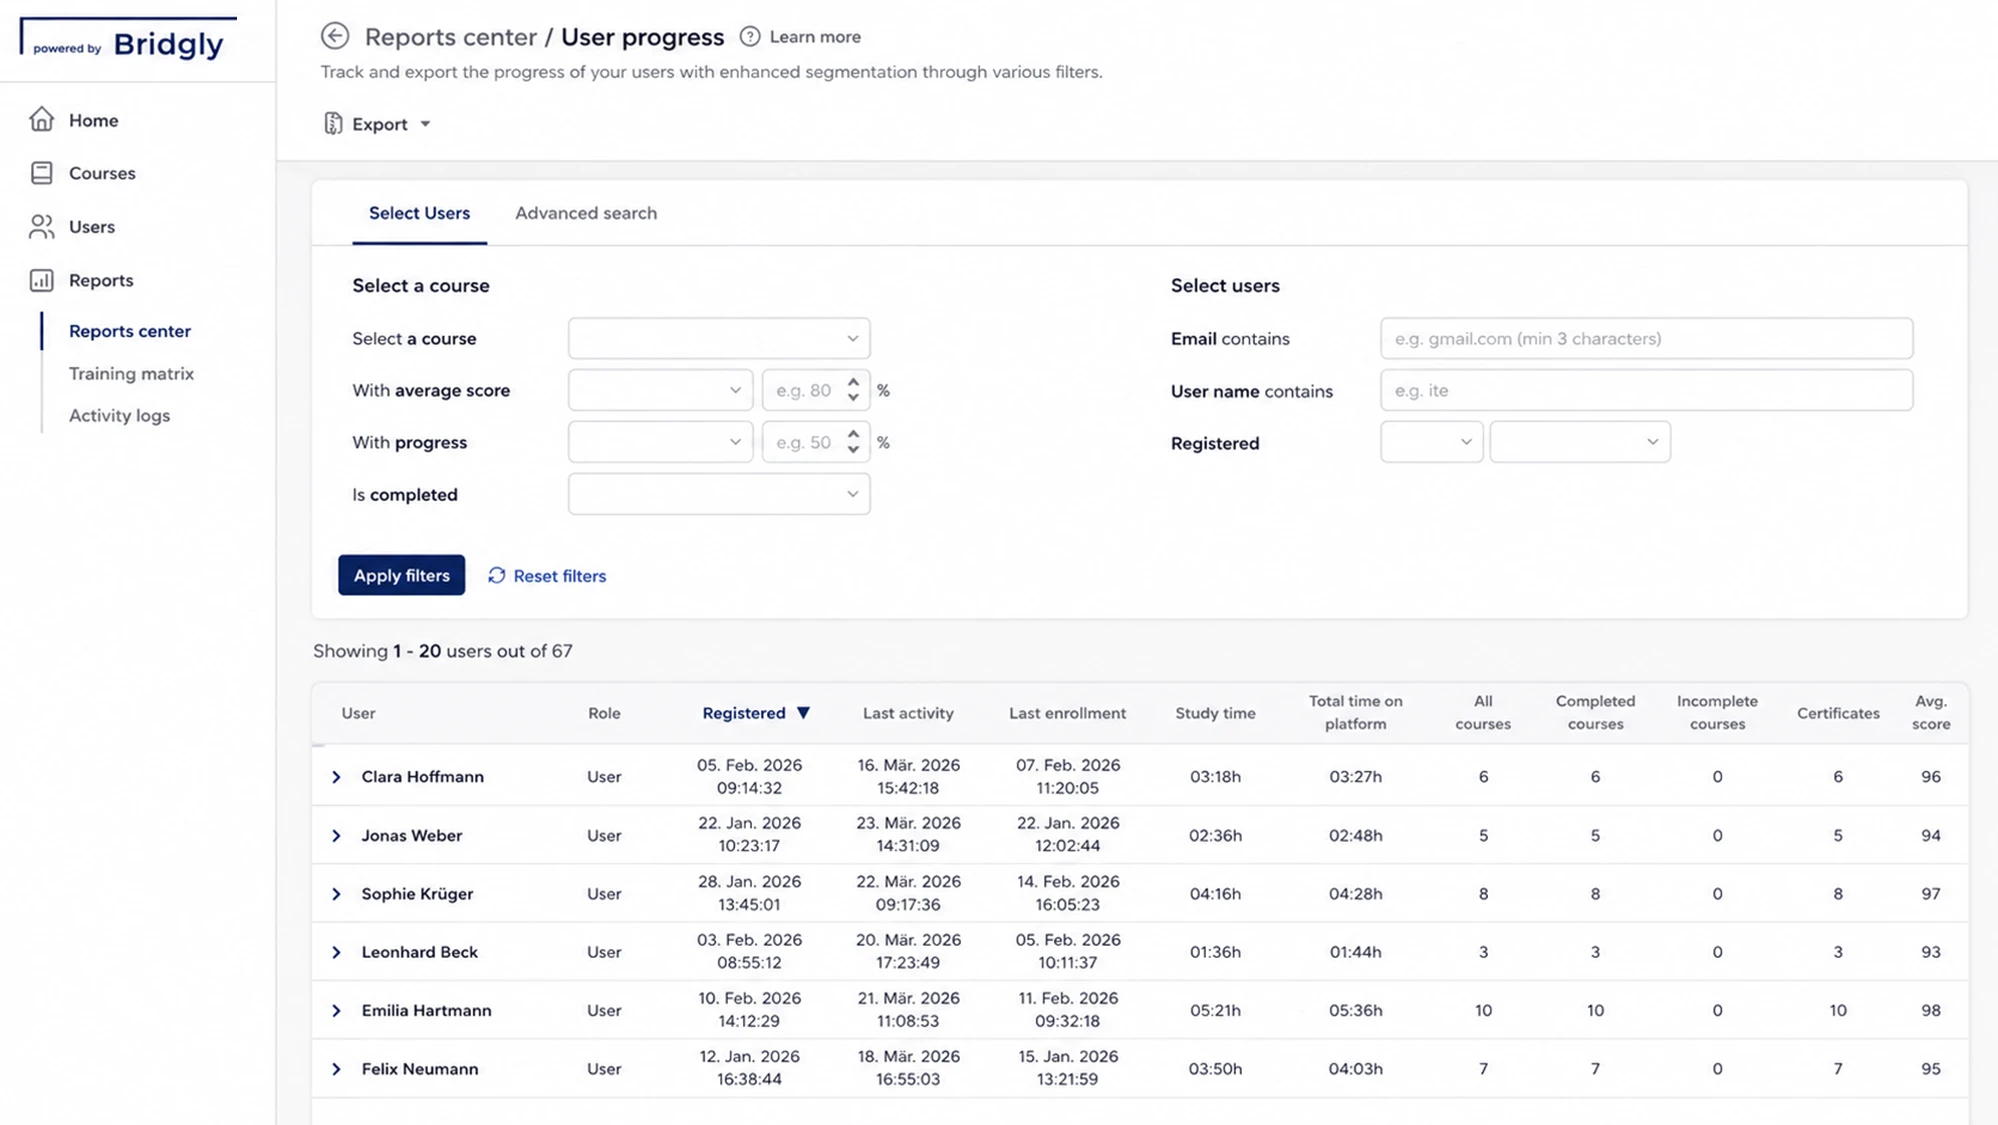
Our platform bundles all training management functions, from planning to reporting, in one place.
Training organization
Define who is trained on which content and when.
Training documentation
See at any time who completed which content and when.
Manage participants
CSV import, learning groups, and access rights in one place.
Automated
reminders
Deadlines and recurring training run automatically.
Here you will find the most important answers.
Yes — in practice, even though the GDPR does not set out an explicit training obligation for all employees. Article 39 (1) lit. b GDPR obliges the data protection officer to raise awareness among and train the staff involved in processing operations. In addition, there is Article 32 GDPR: it requires appropriate technical and organisational measures, and training is one of the key organisational measures. The accountability obligation under Article 5 (2) requires that compliance with the data protection principles can be demonstrated — without documented training, this proof is hardly possible. Supervisory authorities therefore regularly assess a lack of employee training as a separate violation, not merely as an aggravating circumstance.
The most common attack vectors target people, not technology. They include: Phishing and spear phishing — messages that harvest login credentials; CEO fraud — fake instructions from supposed superiors; Ransomware — encryption after clicking on an attachment or link; Social engineering — manipulation by phone, chat, or in person; weak and reused passwords; mobile devices, removable media, and open Wi-Fi networks. Effective training teaches the warning signs and safe behavior with emails, passwords, and data — and, above all, clear reporting channels. The time between incident and report determines the extent of the damage.
It aggravates the consequences considerably. Supervisory authorities regard missing training as a violation of the accountability obligation (Article 5 (2) GDPR) and of the obligation to take organisational measures (Article 32 GDPR). Violations of Article 32 are subject to the range of fines under Article 83 (4) GDPR: up to 10 million euros or 2% of worldwide annual turnover, whichever is higher. The frequently cited higher range of 20 million euros or 4% under paragraph 5 concerns other violations, for example of the processing principles or data subject rights. In addition, there are claims for damages by data subjects under Article 82 GDPR and reputational damage. In practice, the first question after an incident is almost always whether it can be proven that employees were trained.
The NIS-2 Directive has been transposed in Germany: the amended BSIG has been in force since December 6, 2025. Since then, the German provisions have been decisive, no longer the articles of the Directive. Section 30 (2) no. 7 BSIG lists "basic training and awareness measures in the field of information technology security" as one of ten risk management measures that the entities concerned must take. This obligation is subject to fines. In addition, Section 38 BSIG applies to management: they must implement the measures and monitor their implementation (subsection 1), are liable for breaches of duty under the rules of company law (subsection 2), and must themselves regularly participate in training (subsection 3). The range of fines is tiered: up to 10 million euros for particularly important entities, up to 7 million euros for important entities. Turnover-based fines only apply above a total turnover of 500 million euros.
At least once a year — even though neither the GDPR nor the BSIG prescribes a fixed interval. Supervisory authorities and the relevant standards ISO/IEC 27001 and BSI Grundschutz consistently assume an annual cycle. The reason lies in the content: attack methods and legal requirements change continuously, and one-off training quickly becomes outdated. In addition, training must be provided when specific occasions arise — when new IT systems are introduced, after security incidents, in the event of significant legal changes, and when new employees join. For particularly exposed areas such as IT administration, HR, and accounting, shorter intervals and in-depth modules are advisable.
In objective, depth, and target audience. Employee training is awareness raising: in around 20 to 45 minutes, it teaches the principles of the GDPR, data subject rights, handling personal data in day-to-day work, what to do in the event of data breaches, and the internal contact persons. Qualification as a data protection officer is specialist training over several days. It covers legal bases, technical and organisational measures, data protection impact assessment, processing on behalf of controllers, international data transfers, and communication with supervisory authorities. They also differ legally: the expert knowledge of the data protection officer is a prerequisite for designation under Article 37 (5) GDPR and is linked to an ongoing obligation of continuing professional development. In Germany, a data protection officer must be designated under Section 38 of the Federal Data Protection Act (BDSG) as soon as at least 20 persons are, as a rule, constantly engaged in automated processing.
Training and professional development for companies and public-sector clients – with audit-proof documentation and a practical focus.
Get in touch nowNote: Some text, images, and videos on this website were generated using artificial intelligence.
All content is for informational purposes and has been carefully reviewed from a journalistic perspective, but does not claim to be exhaustive or legally binding.