S104
·
Weiterbildung

DORA: IT Risk Management in Banks and Insurance Companies

The Digital Operational Resilience Act has applied directly to banks, insurance companies, and other financial entities since January 2025. You learn about ICT risk management, incident reporting, resilience testing, and third-party risk management.

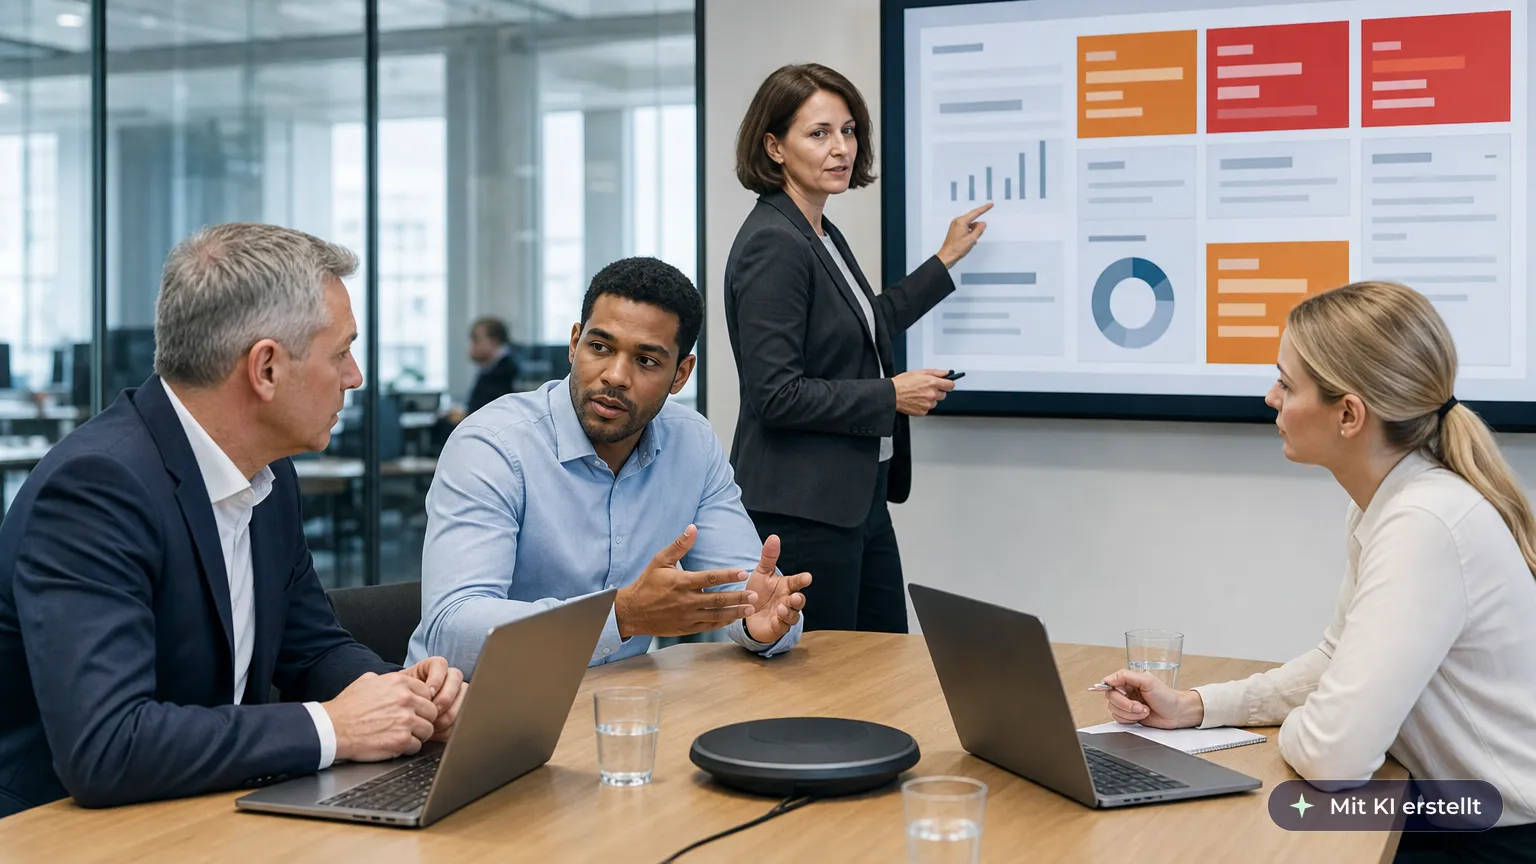
Risk manager runs an emergency drill at a status screen while a board member and the head of IT discuss
Duration

55 min

Format

Multimodal

Languages

Über 30 Sprachen

Proof

Teilnahmebescheinigung

Challenge

Since January 17, 2025, DORA (Regulation (EU) 2022/2554) has applied directly to credit institutions, insurance companies, investment firms, payment service providers, and other financial entities. The Regulation requires ICT risk management, the reporting of major ICT-related incidents within tight deadlines, regular resilience testing, and strict management of ICT third-party service providers, including a register of information. The management body bears full responsibility and must be demonstrably trained, and supervisors are already reviewing implementation.

Learning objectives
  • You have an overview of the scope, structure, and five pillars of DORA.
  • You understand the requirements for the ICT risk management framework and the responsibility of the management body.
  • You know the classification, reporting deadlines, and reporting content for ICT-related incidents.
  • You know the requirements for digital operational resilience testing, including TLPT.
  • You manage ICT third-party service providers contractually, maintain the register of information, and know the oversight framework for critical providers.
Agenda
00 Dora - Fundamentals
01 Governance
02 ICT risk management framework
03 Risk identification
04 Protection, prevention, and detection
05 Response and recovery
06 Backup and recovery
07 Learning, evolving, and communication
08 Management of ICT third-party risks
09 Critical ICT service providers
10 Relevant certifications of service providers
11 Summary
12 Knowledge check incl. certificate of completion

‍

‍

Target group

Executive management, IT, risk, and compliance officers, as well as outsourcing officers in banks, insurance companies, and other financial entities.

Leading organizations trust Bridgly

Logo von Ols
Logo von Ols
Logo von Ols
You decide where your training course runs.

Deployment of your choice

Bridgly is the easiest way to manage, assign, and document training courses. For existing LMSs, we also provide the training courses in SCORM format.

Easy management

Assign training courses automatically and manage participants, deadlines, and refreshers centrally.

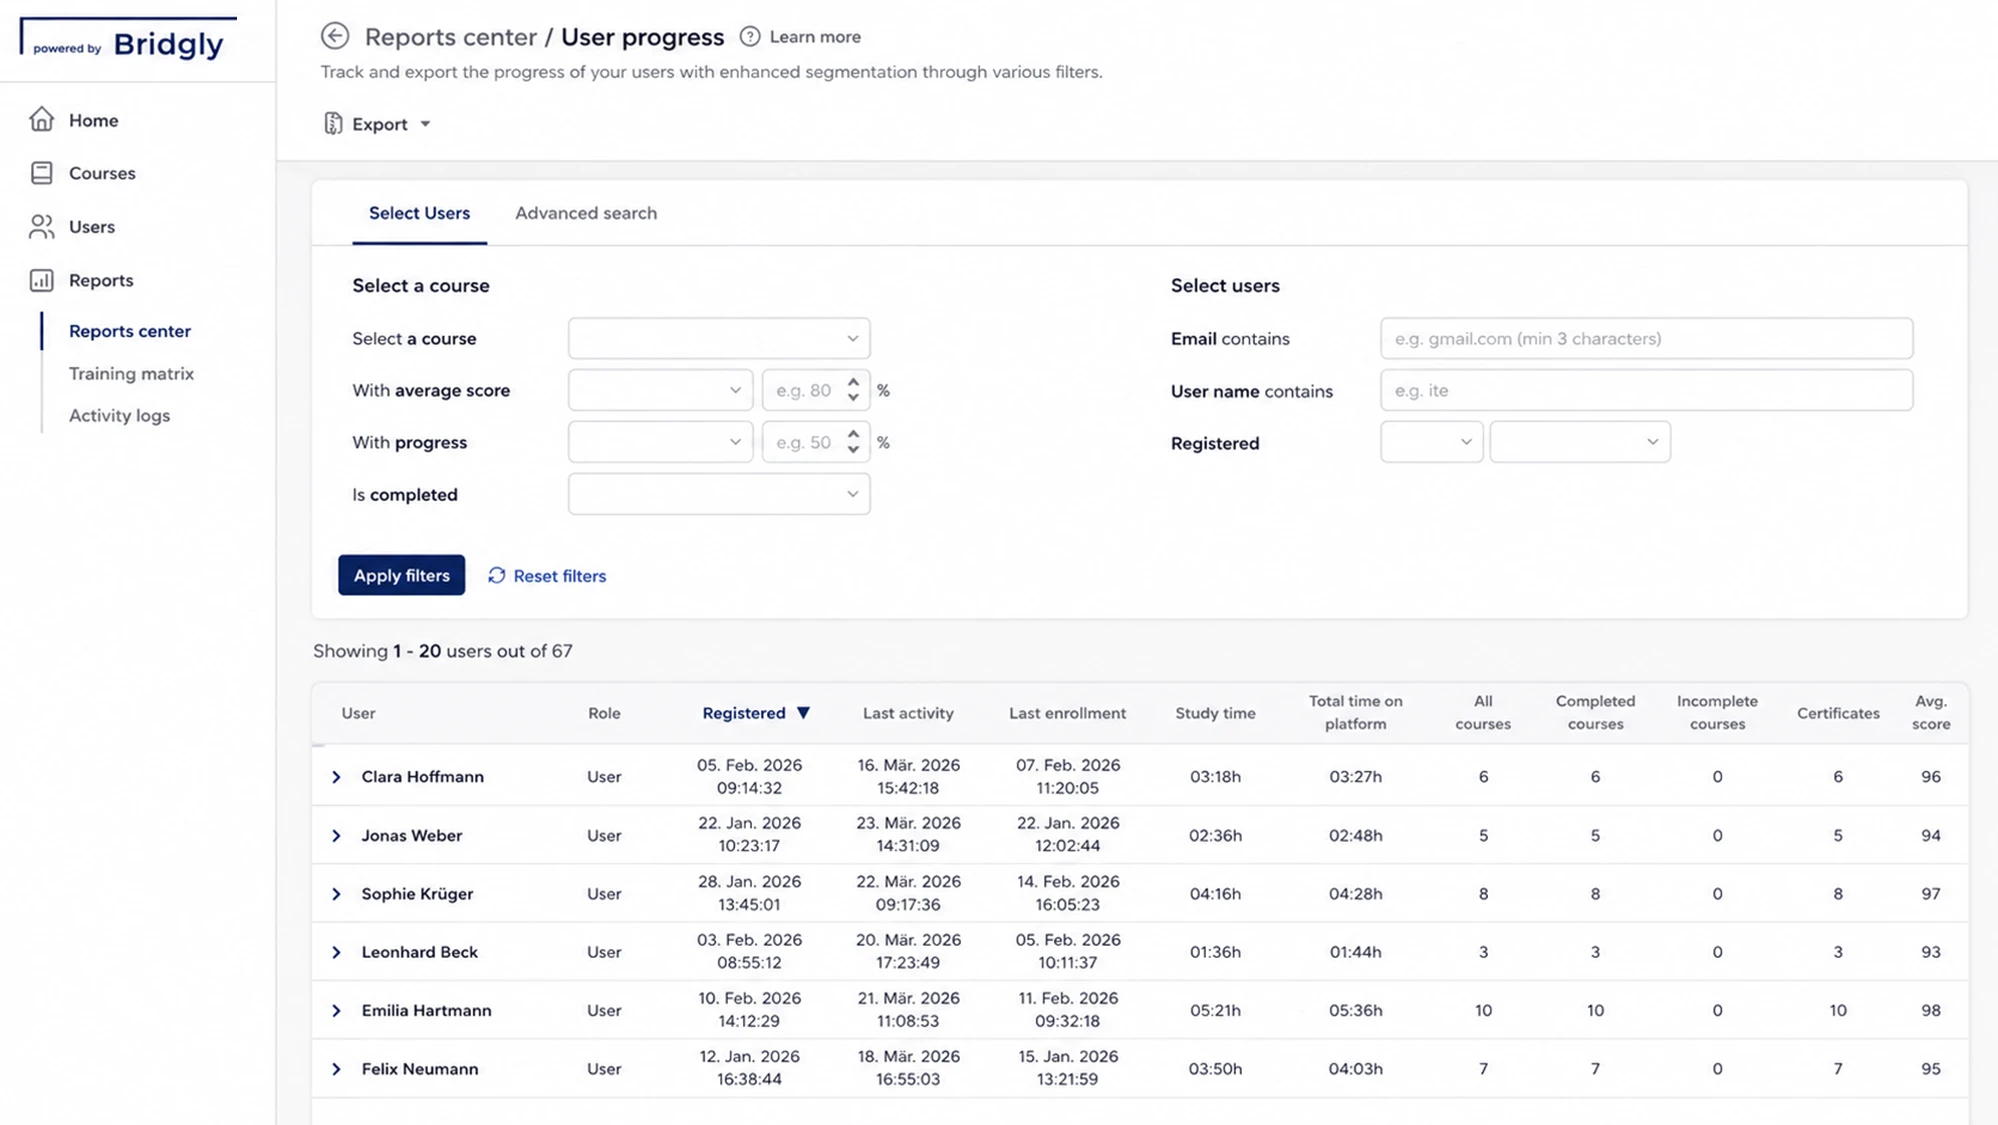
Automated reporting

All participations and completions are documented centrally and can be retrieved at any time for evidence and audits.

FAQ

Frequently Asked Questions

Here you will find the most important answers.

Is data protection training for employees mandatory under the GDPR?
Which cyber threats should companies train their employees on?
What are the consequences of missing data protection training in the event of a data breach?
What training obligations arise from NIS-2 and the BSI Act (BSIG)?
How often must data protection and IT security training be repeated?
How does GDPR training for employees differ from the qualification as a data protection officer?
Contact

Train your employees in a legally compliant and verifiable way

Training and professional development for companies and public-sector clients – with audit-proof documentation and a practical focus.

Get in touch now
Eine Hand blättert in einem grauen Ringordner mit Tabellen, dahinter ein aufgeklappter Laptop

Note: Some text, images, and videos on this website were generated using artificial intelligence.
All content is for informational purposes and has been carefully reviewed from a journalistic perspective, but does not claim to be exhaustive or legally binding.