
With NIS-2, the number of regulated companies in Germany grows to around 30,000 entities. You learn to check whether you are affected and to implement registration and reporting obligations.
55 min
Multimodal
Über 30 Sprachen
Teilnahmebescheinigung
With NIS-2 and the NIS-2 implementation act, the group of regulated companies in Germany is expanded to around 30,000 particularly important and important entities, far beyond the traditional KRITIS (critical infrastructure) operators. Affected companies must register with the BSI, submit an initial report on significant security incidents within 24 hours, implement risk management measures in line with the state of the art, and include the supply chain. Management is liable to its own entity for implementation and is obliged to undergo training.
00 Fundamentals: NIS-2 and the German implementation act
01 Applicability check and registration
02 Reporting obligations for security incidents
03 Risk management measures and supply chain
04 Management obligations, supervision, and sanctions
05 Summary
06 Knowledge check incl. certificate of completion
Management, IT security and compliance managers, and information security officers in potentially affected companies and KRITIS operators.
Leading organizations trust Bridgly


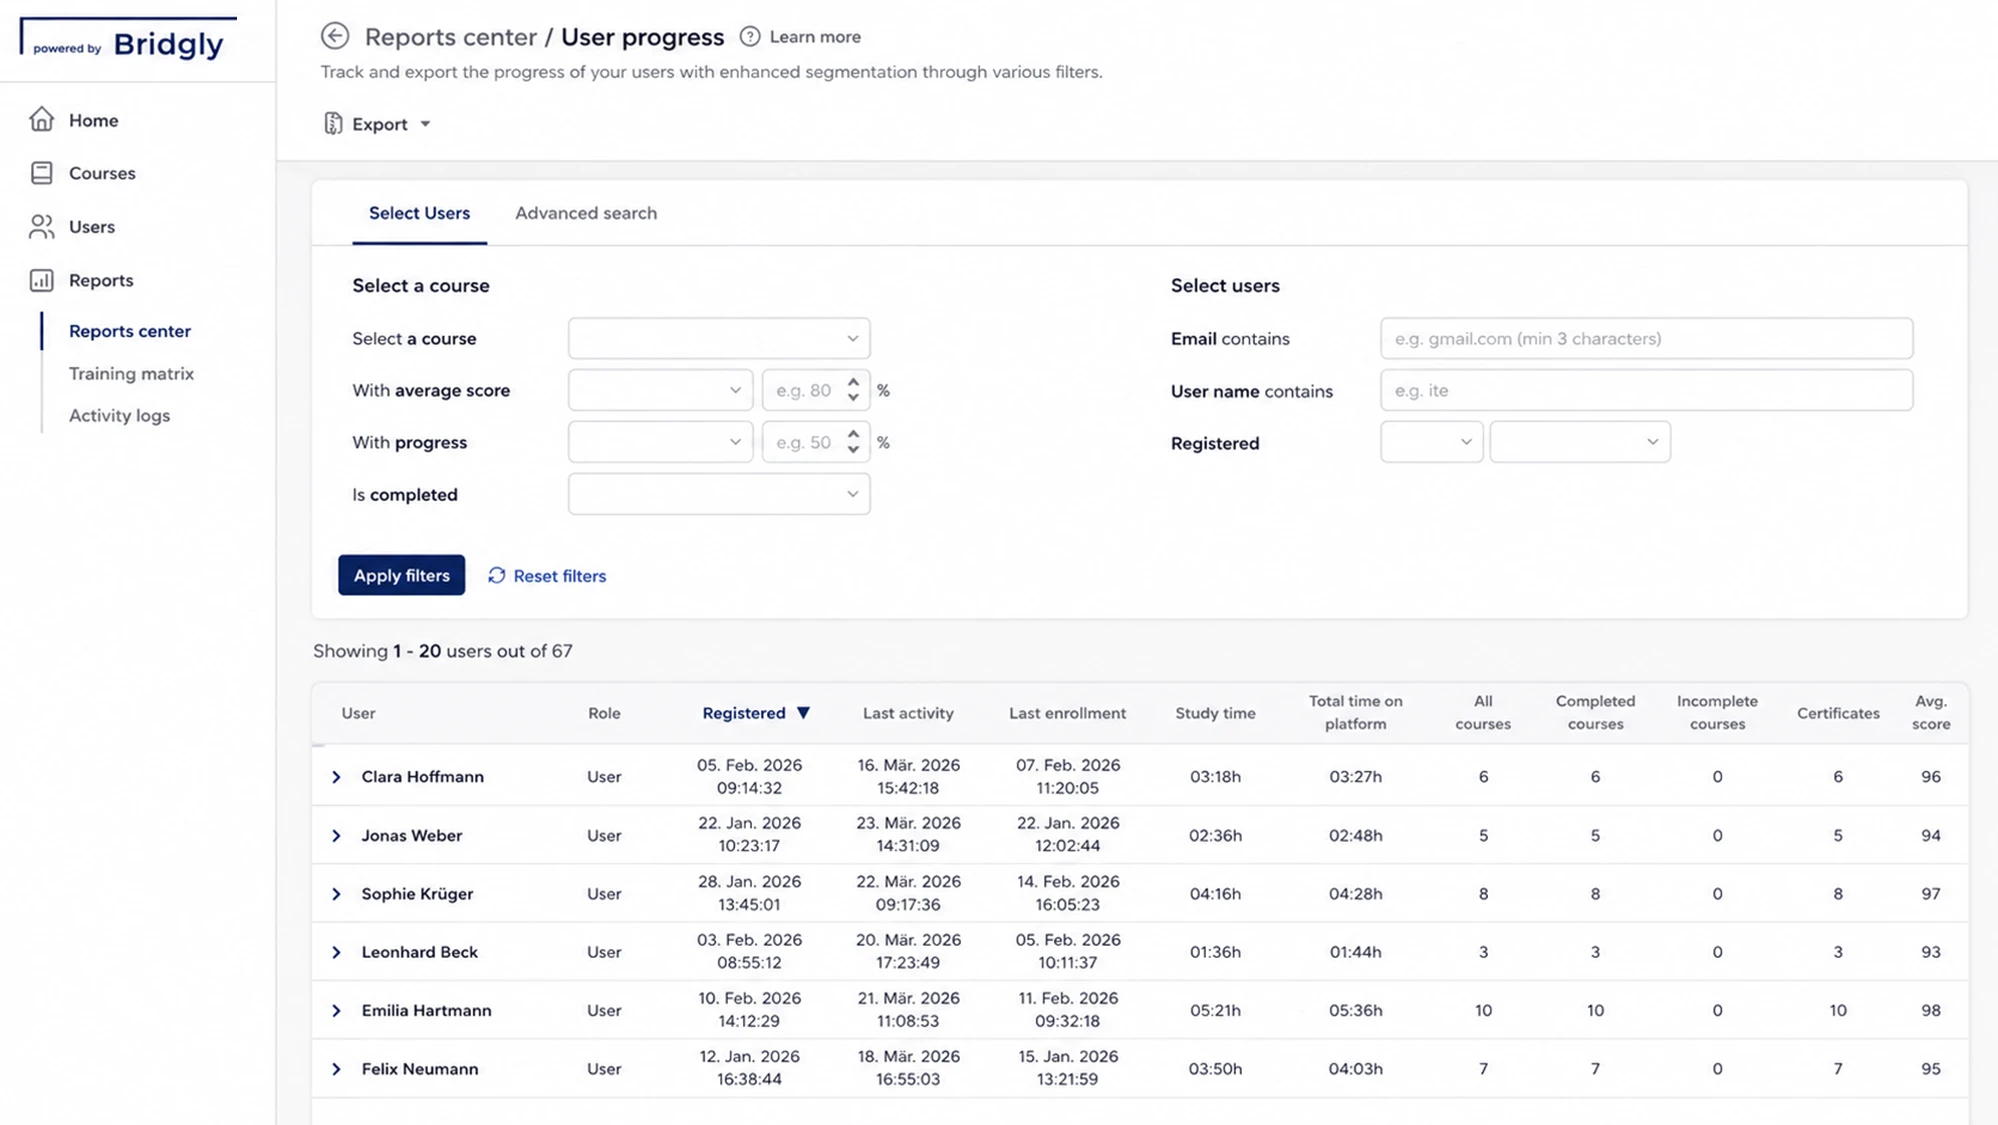
Our platform bundles all training management functions, from planning to reporting, in one place.
Training organization
Define who is trained on which content and when.
Training documentation
See at any time who completed which content and when.
Manage participants
CSV import, learning groups, and access rights in one place.
Automated
reminders
Deadlines and recurring training run automatically.
Here you will find the most important answers.
Training and professional development for companies and public-sector clients – with audit-proof documentation and a practical focus.
Get in touch now
Bridgly is the European training partner for audit-proof, tailored, and automated training and professional development.
 We support the IHK initiative "Pack ma's digital" to help businesses in Upper Bavaria with digitalisation and secure the future of the region.
Note: Some text, images, and videos on this website were generated using artificial intelligence.
All content is for informational purposes and has been carefully reviewed from a journalistic perspective, but does not claim to be exhaustive or legally binding.